Severe PHP Vulnerability Exposes Global Web Infrastructure to Systemic Cyber Risks
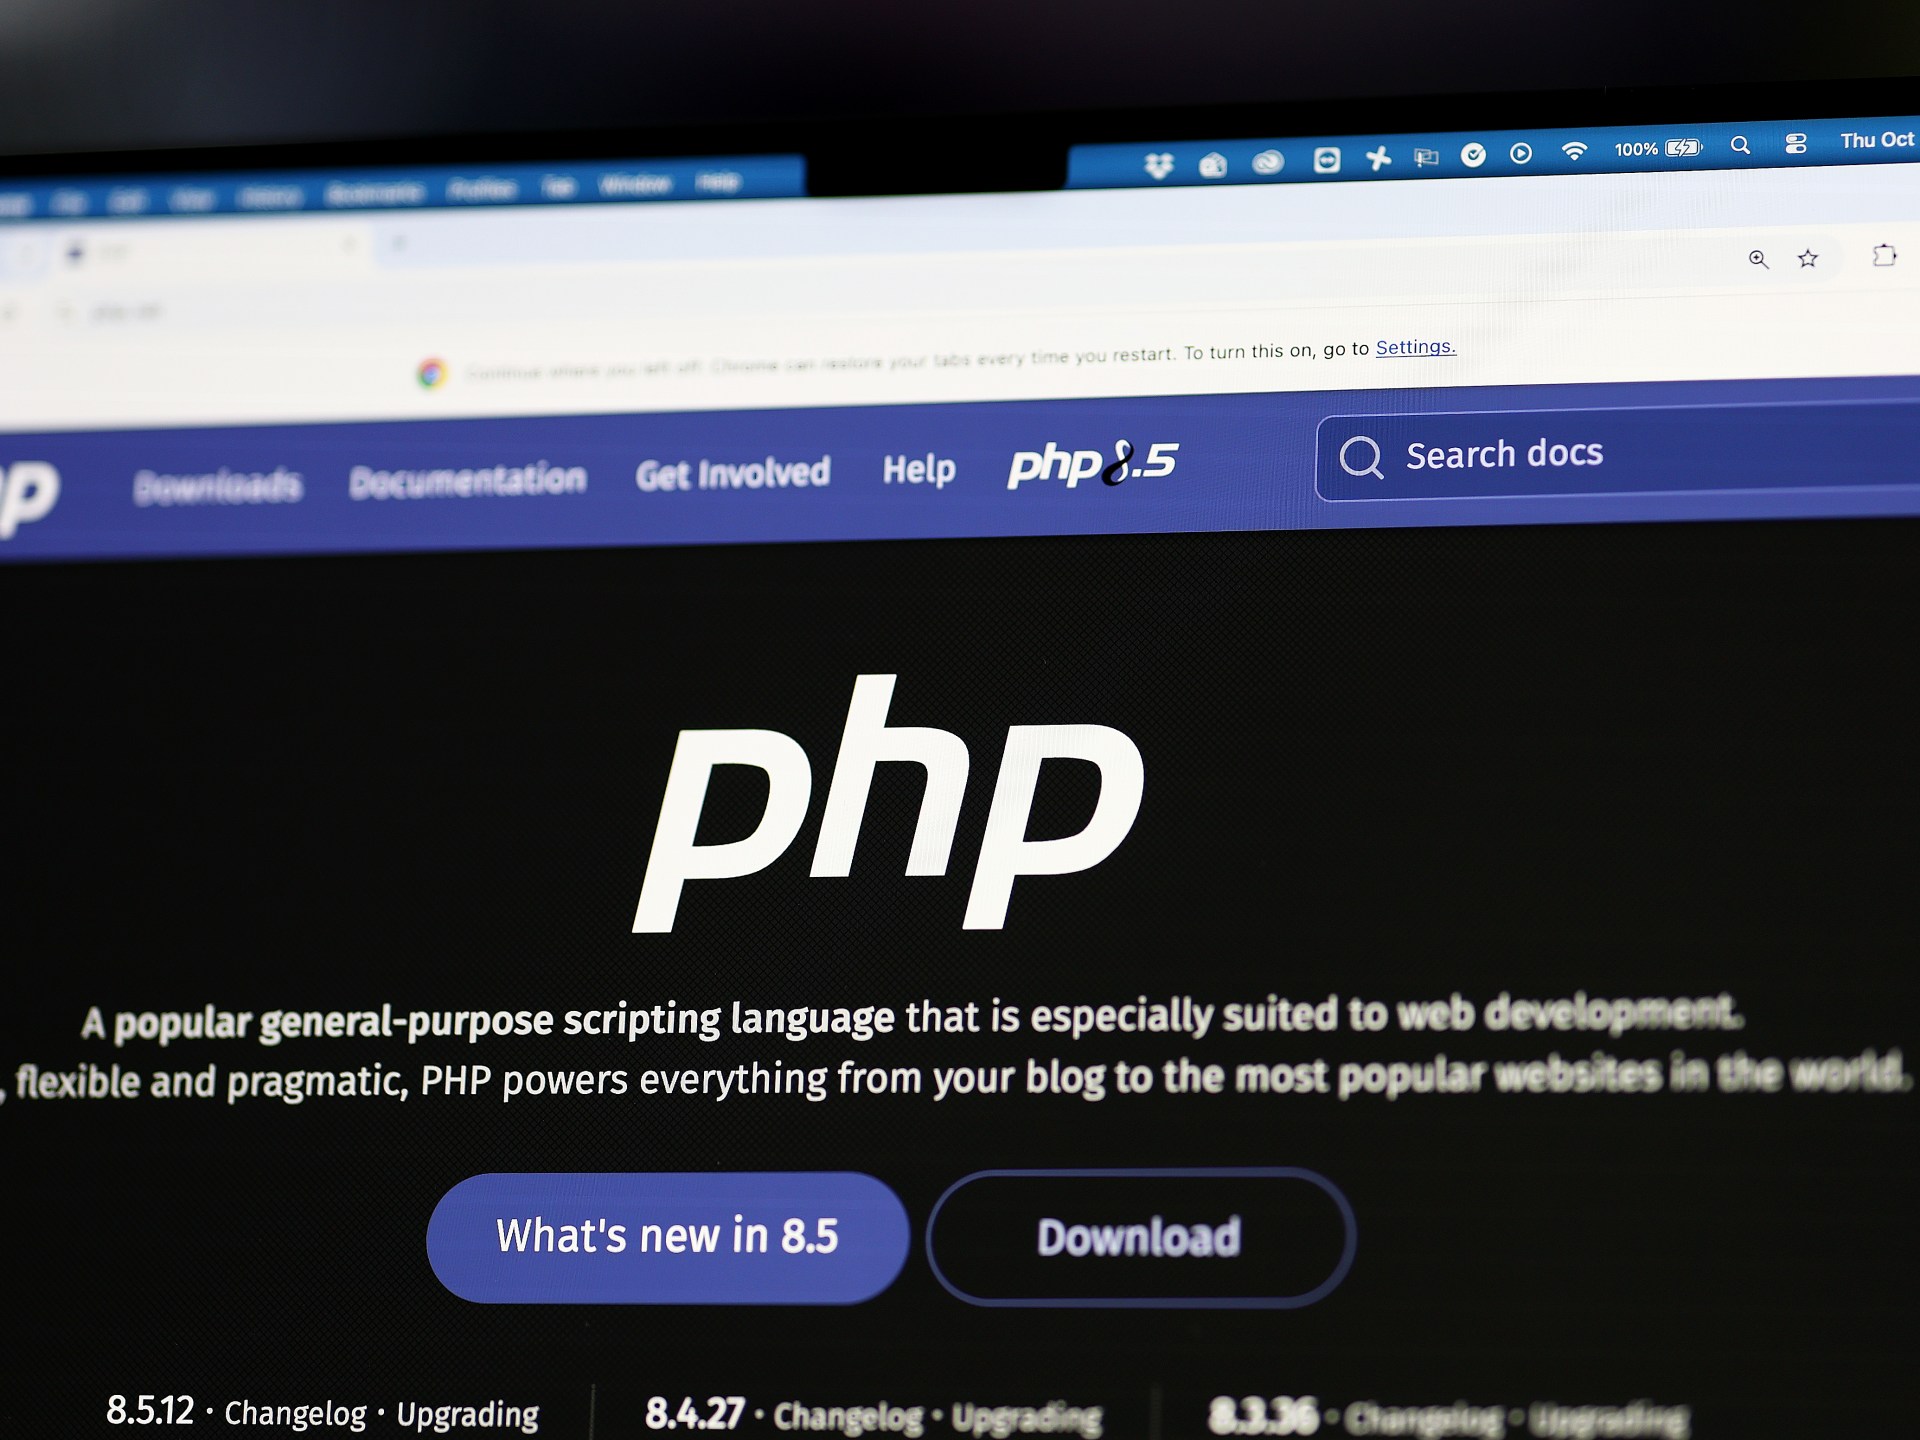
A newly disclosed vulnerability in the ubiquitous PHP programming language threatens up to 70 percent of the internet, prompting urgent security alerts across global supply chains and sovereign cybersecurity agencies.
Geopolitical & Core Developments
A critical vulnerability discovered in the foundational architecture of PHP—the server-side programming language powering approximately 70 percent of the world's public-facing websites—has triggered widespread alerts across international cybersecurity agencies and state defense apparatuses. The flaw fundamentally undermines the integrity of web applications by granting malicious threat actors the capability to execute arbitrary code, alter digital platform interfaces, and exfiltrate proprietary corporate records alongside private personal data.
The strategic stakes surrounding this disclosure extend far beyond conventional technical remediation. In modern hybrid conflict environments, advanced persistent threat groups affiliated with state intelligence services routinely exploit structural vulnerabilities within widely distributed open-source tools. With nation-state actors actively seeking leverage over adversaries through asymmetric digital strikes, the exposure of core web systems presents an immediate threat to sovereign digital infrastructure, municipal public utilities, and sensitive administrative databases worldwide.
Global Trade & Economic Ripples
The economic implications of an architectural failure across widespread web infrastructure are extensive, threatening the resilience of international commerce and cross-border settlement channels. Modern commercial ecosystems, ranging from international commodity trading portals to maritime shipping management suites, rely heavily on legacy web frameworks constructed over PHP environments. Exploitation of these vectors can destabilize container vessel scheduling, halt digital customs documentation processing, and disrupt spot commodity price discovery mechanisms.
Furthermore, transnational retail networks and corporate enterprise resource planning software run the acute risk of data integrity loss. Should widespread unauthorized intrusions occur, supply chains would face systemic friction, inflating operational logistics costs and triggering substantial insurance liabilities across global risk-underwriting syndicates. In financial markets, sudden disruptions to transaction clearing systems undermine short-term liquidity, accelerating corporate expenditure toward emergency cyber defense while depressing near-term capital deployments into operational expansions.
Related Intelligence: Southeast Asia Haze Crisis Strains ASEAN Diplomacy and Agricultural Supply Chains
International Reactions & Diplomatic Stances
International regulatory bodies and sovereign cyber authorities have responded with coordinated advisories, urging system administrators to apply vendor mitigation patches without delay. Agencies including the United States Cybersecurity and Infrastructure Security Agency, alongside European Union cybersecurity monitors, have placed critical infrastructure operators on heightened vigilance, cautioning that automated exploitation frameworks could propagate across unpatched networks rapidly.
Market analysts and institutional technology consultants have similarly warned that the sheer prevalence of unmanaged open-source dependencies poses a systemic liability for sovereign risk profiles. During recent multilateral dialogues on international norms in cyberspace, delegations underscored the imperative for transparent vulnerability disclosures, while privately acknowledging that state-aligned offensive cyber units frequently weaponize zero-day disclosures prior to universal enterprise remediation.
Strategic Outlook & Future Scenarios
Looking ahead, the global response to this vulnerability will serve as a bellwether for international cyberspace governance and corporate digital resilience. The most immediate trajectory involves an aggressive race between security administrators deploying emergency server patches and automated threat vectors scanning global IP address spaces for unfortified web assets. Incomplete patch compliance across mid-tier commercial enterprises will leave lingering backdoors, creating persistent vectors for corporate espionage and data hostage operations.
In the medium term, this incident is expected to intensify legislative momentum across leading economies to mandate standardized software supply chain transparency, enforcing strict vendor liability for software dependencies. Multilateral institutions will increasingly treat core digital infrastructure standards as critical components of national economic defense, driving greater integration between sovereign cybersecurity policies and international trade compliance frameworks.
Join Our Official WhatsApp Channel
Receive live commodity alerts, policy changes, and commercial intelligence directly on WhatsApp.